Best AI Regulatory Compliance Tools for Businesses (2026)
No piece of software makes a company compliant with an AI law. What the software does is produce the inventory, risk assessments, records and monitoring that let your people show a regulator, an auditor or a court that they are in control of the systems they deploy. That distinction matters more in 2026 than it did when I first wrote this post, because the market has exploded, the deadlines have moved, and the first independent analyst ranking of the category has only just appeared.
In June 2026, Gartner published its first Magic Quadrant for AI Governance Platforms, a sign the category has matured from a loose collection of products into a market of its own. This guide explains what changed in the law, what these tools really do, how the leading vendors differ, and how to choose without being swayed by marketing. I have rewritten it from scratch and removed several claims from the 2024 version that have changed. The update note at the end lists exactly what I corrected.
Key takeaways
- The top EU AI Act fine is 35 million euros or 7 percent of worldwide turnover, whichever is higher, for prohibited practices.
- EU high-risk obligations now apply from 2 December 2027 (stand-alone systems) and 2 August 2028 (embedded in regulated products), after the AI Omnibus.
- In the United States, the compliance burden sits with the states. Colorado’s law was repealed and re-enacted in May 2026 and now takes effect on 1 January 2027.
- Gartner’s June 2026 Magic Quadrant named IBM, ServiceNow and Truyo as Leaders among 13 vendors, but a placement is not proof a product will satisfy an auditor.
- Smaller organisations should often start with a framework (NIST AI RMF or ISO/IEC 42001) and a simple AI inventory before buying a platform.
Understanding the AI Regulatory Landscape in 2026
European Union
The EU AI Act (Regulation (EU) 2024/1689) remains the global reference point, and its penalty structure is the clearest incentive to invest in compliance. Under Article 99, breaches of the prohibited practices can draw fines of up to 35 million euros or 7 percent of total worldwide annual turnover, whichever is higher. Most other operator obligations carry fines of up to 15 million euros or 3 percent, and supplying incorrect or misleading information to authorities carries up to 7.5 million euros or 1 percent. For small and medium-sized enterprises the lower of the two figures applies.
The timetable has changed. Regulation (EU) 2026/1744, the AI Omnibus, entered into force on 27 July 2026. It moves the application date for stand-alone high-risk systems under Annex III from 2 August 2026 to 2 December 2027, and for AI embedded in regulated products to 2 August 2028. The prohibitions have applied since February 2025. A tool vendor still telling you the August 2026 high-risk deadline is imminent is working from outdated material.
United States
There is still no comprehensive federal AI statute that I am aware of, and the compliance picture is a state patchwork. Executive Order 14110 was revoked in January 2025, and a December 2025 executive order directs the Justice Department to challenge state AI laws. According to a law firm update from 1 October 2026, that order does not itself preempt state law, no federal court has enjoined a state statute on the strength of it, and state laws remain in effect.
The state laws that matter most for businesses deploying AI are these. Texas’s Responsible AI Governance Act (TRAIGA) and Illinois’s HB 3773, which covers discrimination in employment decisions, both took effect on 1 January 2026. California’s SB 53 targets developers of frontier models and also began on 1 January 2026. Colorado is the most unstable: its original law was delayed to 30 June 2026, and then SB 26-189, signed on 14 May 2026, repealed and re-enacted it with an effective date of 1 January 2027, shifting the focus towards automated decision-making technology. The same law firm update reports that Connecticut’s CART Act takes effect on 1 October 2026. Texas’s law also refers to the NIST AI Risk Management Framework as a factor in showing compliance, which is one reason aligning with that framework is a sensible default.
Standards and the rest of the world
Two voluntary frameworks sit underneath almost every platform on the market. The NIST AI Risk Management Framework (published as NIST AI 100-1) provides a risk-management vocabulary used widely in the United States, and ISO/IEC 42001 is the international standard for an AI management system and the basis for third-party certification. Outside these, the position in the United Kingdom, as far as I am aware at the time of writing, remains sector-regulator-led and combined with data protection law rather than a single AI statute. If you sell into the EU or US, you are covered by those regimes regardless of where you are based.
What AI Compliance Tools Do, and What They Do Not
Vendors marketing themselves as “AI governance platforms” do very different jobs, and most buying mistakes come from confusing them. Recent buyer guides group the market into a handful of categories. Policy and risk management platforms such as Credo AI, Trustible and Holistic AI turn regulations into controls and assessments. Incumbent governance, risk and compliance extensions, such as OneTrust, ServiceNow and IBM, bolt AI inventory and vendor risk onto platforms organisations already use. Runtime enforcement tools and AI gateways control what models and agents can actually do. Observability specialists such as Fiddler AI and Arthur AI monitor performance, drift and bias in production. A few, notably the privacy-led vendors, start from whether the personal data inside an AI system was lawfully collected.
What none of them can do is decide your legal obligations. A platform can tell you that a chatbot sits in a limited-risk tier or that a hiring model needs an impact assessment, but classification depends on facts and judgement, and a wrong answer in the software is still your wrong answer. Treat the tool as an evidence system and a workflow engine, and keep a lawyer in the loop for classification and for any contested question. The cases in my article on AI ethics failures and the 2026 legal landscape show what regulators and courts have actually punished: missing testing, missing monitoring and missing accountability, not missing software.
The 2026 Market: Gartner’s First Magic Quadrant
On 16 June 2026, Gartner published the first Magic Quadrant for AI Governance Platforms, a report that vendors have been quick to publicise as the category’s first. It assessed 13 vendors. Based on the vendors’ own announcements, ServiceNow and Truyo were named Leaders, alongside IBM, which plotted highest of the three. OneTrust, Credo AI, Monitaur, Airia and ModelOp were placed as Visionaries, and Holistic AI as a Challenger. Modulos received an honorable mention.
I would use this as a shortlist-building aid and nothing more. A Magic Quadrant ranks vendors on ability to execute and completeness of vision as Gartner defines them. It does not test whether a product will produce the evidence a specific regulator or auditor wants, vendors choose how loudly to promote their placement, and the full report sits behind a registration form. Read it for the criteria and the cautions, then run your own pilot.
Top AI Governance and Compliance Tools for 2026
The list below covers the vendors that appeared in the Gartner assessment and are most often shortlisted by enterprises, with an honest view of where each tends to fit. Prices are not shown because most vendors quote on request, and the specific monthly prices in my 2024 version could not be verified, so I removed them.
IBM watsonx.governance
IBM plotted highest among the Gartner Leaders, and it is the conventional choice for large, regulated organisations running hybrid estates. It governs models built on IBM and third-party platforms, and comparison guides cite accelerators aligned to the EU AI Act, ISO/IEC 42001, NIST and the US banking model-risk guidance SR 11-7. IBM also resells Credo AI policy packs as a compliance add-on. The trade-off reported by independent comparisons is that the value is highest inside the IBM ecosystem and the learning curve is steep, so test integration effort before you commit.
ServiceNow AI Control Tower
A Gartner Leader, and the obvious extension for organisations that already run workflow on ServiceNow, because AI inventory, approvals and incidents sit alongside existing IT and risk processes. Its 2026 enhancements focus on agents, including detecting an agent acting beyond its permissions and stopping it in real time. Reviewers noted these features were due for general availability in August 2026, so ask for production references rather than demonstrations.
Truyo
The third Leader, and the one that comes to the category from data privacy and consent management. That heritage suits teams whose AI governance problem starts as a question about personal data, such as whether data in a model was collected lawfully and whether individuals can exercise their rights.
Credo AI
Placed as a Visionary by Gartner and named a Leader in the Forrester Wave for AI governance solutions in the third quarter of 2025. Credo is built for the people who write policy rather than code, and its strength is translating regulations and frameworks into control sets and assessments. It is a strong candidate when your main need is a governance programme of record for the EU AI Act, ISO/IEC 42001 and NIST.
OneTrust AI Governance
A Visionary, and the natural extension for organisations whose privacy programme already runs on OneTrust. It automates discovery and registration of models, datasets, vendors and agents, and the company is pushing hard into runtime governance, meaning detection of policy violations across supported AI platforms rather than periodic review alone.
Holistic AI
Gartner placed it as a Challenger. It originated at University College London and differs from many platforms by doing technical assessment itself, including bias testing and audits, and by discovering shadow AI across an organisation’s endpoints rather than waiting for teams to register their systems. That makes it useful when you suspect you do not yet know what AI is in use.
Monitaur, Airia and ModelOp
Monitaur concentrates on audit-ready assurance for regulated sectors. Airia pairs governance with AI security and says it ranked first for the AI security use case in Gartner’s companion Critical Capabilities report, which is a vendor claim worth verifying. ModelOp is an enterprise model-lifecycle governance specialist. All three were placed as Visionaries.
Other names worth knowing
The assessed vendors also included SAP, Saidot, Cranium AI and Relyance AI, which were plotted among the niche players, and Modulos, a Zurich-based risk-centric platform. For runtime monitoring, observability specialists such as Fiddler AI and Arthur AI are commonly paired with a governance platform. The large cloud providers also ship governance features inside their own AI platforms, which are worth evaluating first if your models already live there. The cloud-specific products named in my 2024 version were removed because I could not verify them.
How to Choose the Right Tool
Start from your own position, not from the quadrant. Are you mainly a deployer of third-party AI, a developer of your own models, or both? Under the EU AI Act the obligations differ, and a business that only buys and configures software has a very different tooling need from one that trains models. Then look at the systems you already own: the cheapest and fastest governance programme is usually the extension of a platform your teams already use.
| If your situation is… | Start by evaluating… | Why |
|---|---|---|
| Already standardised on ServiceNow, IBM or OneTrust | That vendor’s AI governance module | Reuses workflows, users and vendor risk processes |
| Need one programme of record for EU AI Act, ISO/IEC 42001 and NIST | Credo AI, IBM watsonx.governance, Holistic AI | Regulation-to-control libraries and reporting depth |
| Privacy team leads on AI risk | OneTrust, Truyo | Starts from data collection, consent and rights |
| Security team worries about agents and shadow AI | Airia, ServiceNow, Holistic AI | Discovery and runtime controls |
| Regulated sector needing model assurance and audit trails | Monitaur, ModelOp, IBM | Model-lifecycle evidence for supervisors |
| Small team, few AI systems | A written policy, an AI inventory spreadsheet and the NIST AI RMF | A platform may cost more than the risk it removes |
In demonstrations, press on five things. Ask how the tool discovers AI you have not registered. Ask which regulations and standards are mapped to controls, and who updates those mappings when laws change, since the EU timetable moved this summer. Ask whether it produces evidence in a form an auditor can use, not just dashboards. Ask what it can enforce at runtime and what it can only report. And ask for references from customers in your sector who have been through an audit.
Implementation Strategy
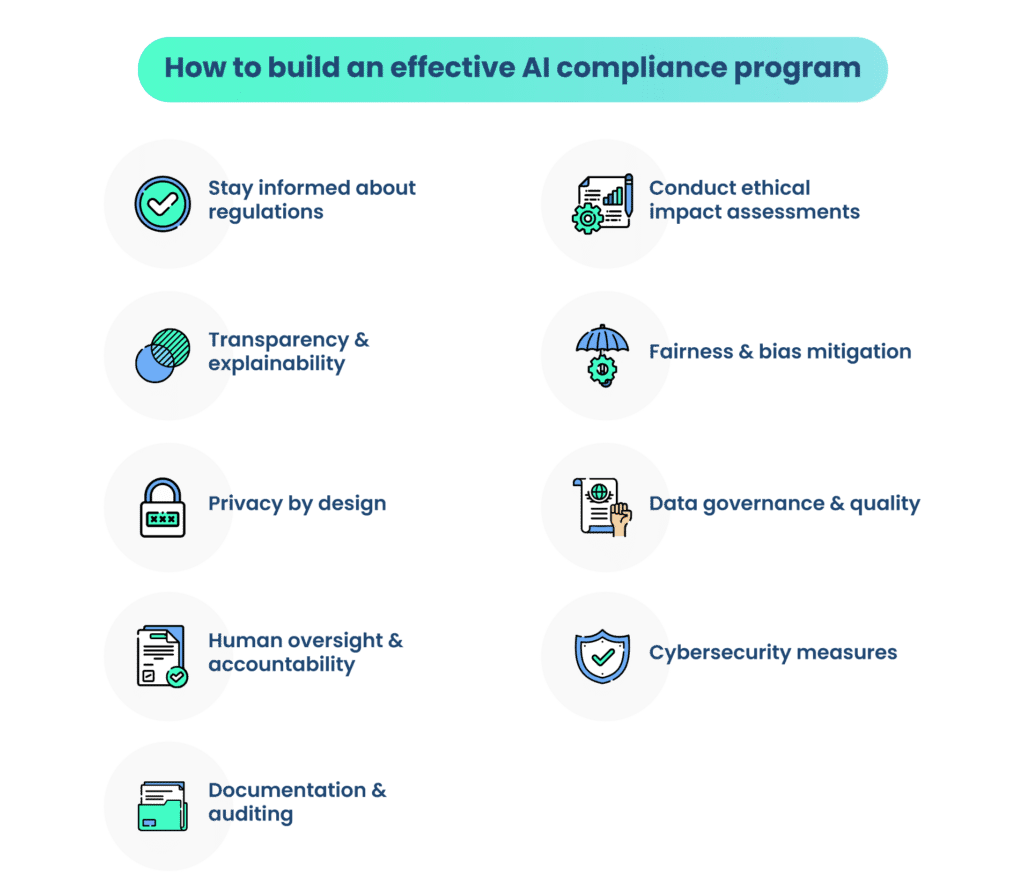
Tools fail when they are bought before the basics exist. Begin with an inventory of every AI system in use, including software your staff adopted without approval, because you cannot classify or assess what you cannot see. Classify each system against the regimes that apply to you, assign a named owner to each, and record the decisions that matter. Map your controls to one framework, such as ISO/IEC 42001 or the NIST AI RMF, so that evidence you gather once serves several regulators.
Pilot on two or three real systems with different risk profiles, for example a customer-facing chatbot and a hiring or credit model, and judge the tool on how much real work it saves and whether its outputs would survive scrutiny. Only then roll it out, with monitoring and an incident process in place. The training and oversight roles matter as much as the software, and I cover the people side in my wider writing on AI safety and governance.
Costs and Return on Investment
My 2024 version quoted a set of precise return-on-investment figures attributed to a Harvard Business Review study. I could not locate that study, so I have removed the figures. Most return-on-investment numbers circulating for governance platforms today come from vendors or vendor-sponsored research, and I would treat them as marketing until you have seen the method.
A more defensible approach is to build your own case from four inputs: the staff time your current manual reviews consume, the value of AI projects delayed in a governance backlog, the cost of the exposure you are managing (the EU fine tiers above are a useful ceiling for the largest breaches, not a forecast), and the cost of licences, integration and the people needed to run the tool. Pricing for the leading platforms is generally quote-based, so get at least two quotes and ask what is included in implementation.
Future-Proofing Your Compliance Strategy
Three trends will shape the next two years. First, governance is moving from periodic review to runtime control, because autonomous agents act faster than a quarterly assessment can follow. Several leading vendors now sell the ability to detect and stop an agent exceeding its permissions, and this is where the market’s differences are widening. Second, the law remains unsettled: the EU deadlines have just moved, Colorado rewrote its law, and the United States is contesting state against federal authority, so choose tools whose regulatory mappings are actively maintained. Third, certification is becoming a signal. ISO/IEC 42001 gives an external attestation that buyers and partners increasingly ask for.
Frequently Asked Questions
Do AI compliance tools make a business compliant with the EU AI Act?
No. They help you inventory systems, assess risk, document controls and monitor performance, but legal classification and accountability remain with your organisation. Treat a tool as an evidence and workflow system, and involve legal counsel for classification.
What is the maximum fine under the EU AI Act?
Up to 35 million euros or 7 percent of total worldwide annual turnover, whichever is higher, for prohibited practices. Other operator obligations carry up to 15 million euros or 3 percent, and supplying incorrect information up to 7.5 million euros or 1 percent. For SMEs the lower figure applies.
When do the EU AI Act’s high-risk obligations apply?
Following the AI Omnibus (Regulation (EU) 2026/1744), from 2 December 2027 for stand-alone high-risk systems under Annex III and from 2 August 2028 for high-risk AI embedded in regulated products.
Is the Colorado AI Act in force in 2026?
No. After earlier delays, SB 26-189, signed on 14 May 2026, repealed and re-enacted the law with an effective date of 1 January 2027 and a focus on automated decision-making technology. Check the current text before relying on any summary.
Which AI governance platform is best?
It depends on your existing systems, your regulators and whether privacy, security or risk teams lead. Gartner’s 2026 Magic Quadrant named IBM, ServiceNow and Truyo as Leaders, but the right choice for you comes from a pilot against your own use cases.
Do I need ISO/IEC 42001 certification?
It is not a legal requirement, but it offers independent evidence of a managed AI governance system, and aligning to a recognised framework such as the NIST AI RMF can also support your position under laws that reference it, such as Texas’s TRAIGA.
Conclusion
The right way to think about AI compliance tools in 2026 is as infrastructure for accountability. The law is moving, sometimes backwards, and a vendor’s claim that its product keeps you compliant should always be tested against the primary sources and against a pilot. Build your inventory, choose a framework, shortlist two or three vendors that fit your existing systems and team, and insist on evidence you can show an auditor. If you want my broader position on AI governance, see my stance on AI, my background and my other articles.
If you would like to remove friction entirely and save yourself a lot of time, then you can hire me as a consultant!
Update note, 27 October 2026. This post was rewritten. Many things have changed in the last 2 years. Corrections to the 2024 version: the top EU AI Act fine (35 million euros or 7 percent, not 40 million euros), the NIST AI Risk Management Framework citation (it is NIST AI 100-1, not Special Publication 800-45), the EU high-risk timetable, and the status of Colorado’s law. I also removed a Gartner statistic and a Harvard Business Review study that I could not trace, the vendor prices and product names I could not verify, and the quantum-resistant security trend.
References
- European Union. (2024). Regulation (EU) 2024/1689 (Artificial Intelligence Act).
- European Union. (2026). Regulation (EU) 2026/1744 (AI Omnibus).
- NIST. (2023). Artificial Intelligence Risk Management Framework (AI RMF 1.0), NIST AI 100-1.
- ISO/IEC. (2023). ISO/IEC 42001:2023 Artificial intelligence management system.
- Baker Botts. (2026). US AI law update: navigating the evolving state and federal regulatory landscape.
- Whiteford. (2026). Client alert: AI governance for businesses.
- Epstein Becker Green. (2026). Colorado SB 26-189 coverage.
- Greenberg Traurig. (2025). Colorado delays comprehensive AI law with further changes anticipated.
- Gartner. (2026). Magic Quadrant for AI Governance Platforms (Kornutick, L., Agarwal, S., Sundararaman, P., Henein, N., & Medford, B.), 16 June 2026. Access via vendor pages: ServiceNow, Truyo, OneTrust, Modulos.
- Stanford HAI. (2026). Artificial Intelligence Index Report 2026.
Further reading
- AI Ethics Case Studies: Lessons Learned from Real-World Failures
- Best AI Ethics Training Programs for Corporations
- 7 Essential Books on AI Governance Every Leader Should Read

Avi is a researcher educated at the University of Cambridge, specialising in the intersection of AI Ethics and International Law. Recognised by the United Nations for his work on autonomous systems, he translates technical complexity into actionable global policy. His research provides a strategic bridge between machine learning architecture and international governance.